AI agent governance
Inventory every AI agent, the identity it acts as and what it can reach, with checks mapped to the OWASP Top 10 for Agentic Applications.
Online version, always current: https://cloudvision360.com/docs/cloudvision360/ai-agent-governance/
AI agents act with real identities and real permissions. CloudVision360 governs them like any other privileged identity.
Every agent, every platform
Inventory AI agents across Microsoft Entra, Copilot Studio, Azure AI Foundry, Amazon Bedrock and Vertex AI — the identity each agent acts as, and what that identity can reach.
The risks it checks for
- Over-privileged agents — an agent whose identity can do far more than its task needs.
- Ownerless agents — no accountable owner.
- Orphaned agents — left behind after a project ended.
Checks are mapped to the OWASP Top 10 for Agentic Applications, so the findings line up with an emerging industry standard.
Governed like other identities
Agent risks appear as findings with owners, risk scores and the same triage and remediation paths as the rest of your identity inventory.
Use it
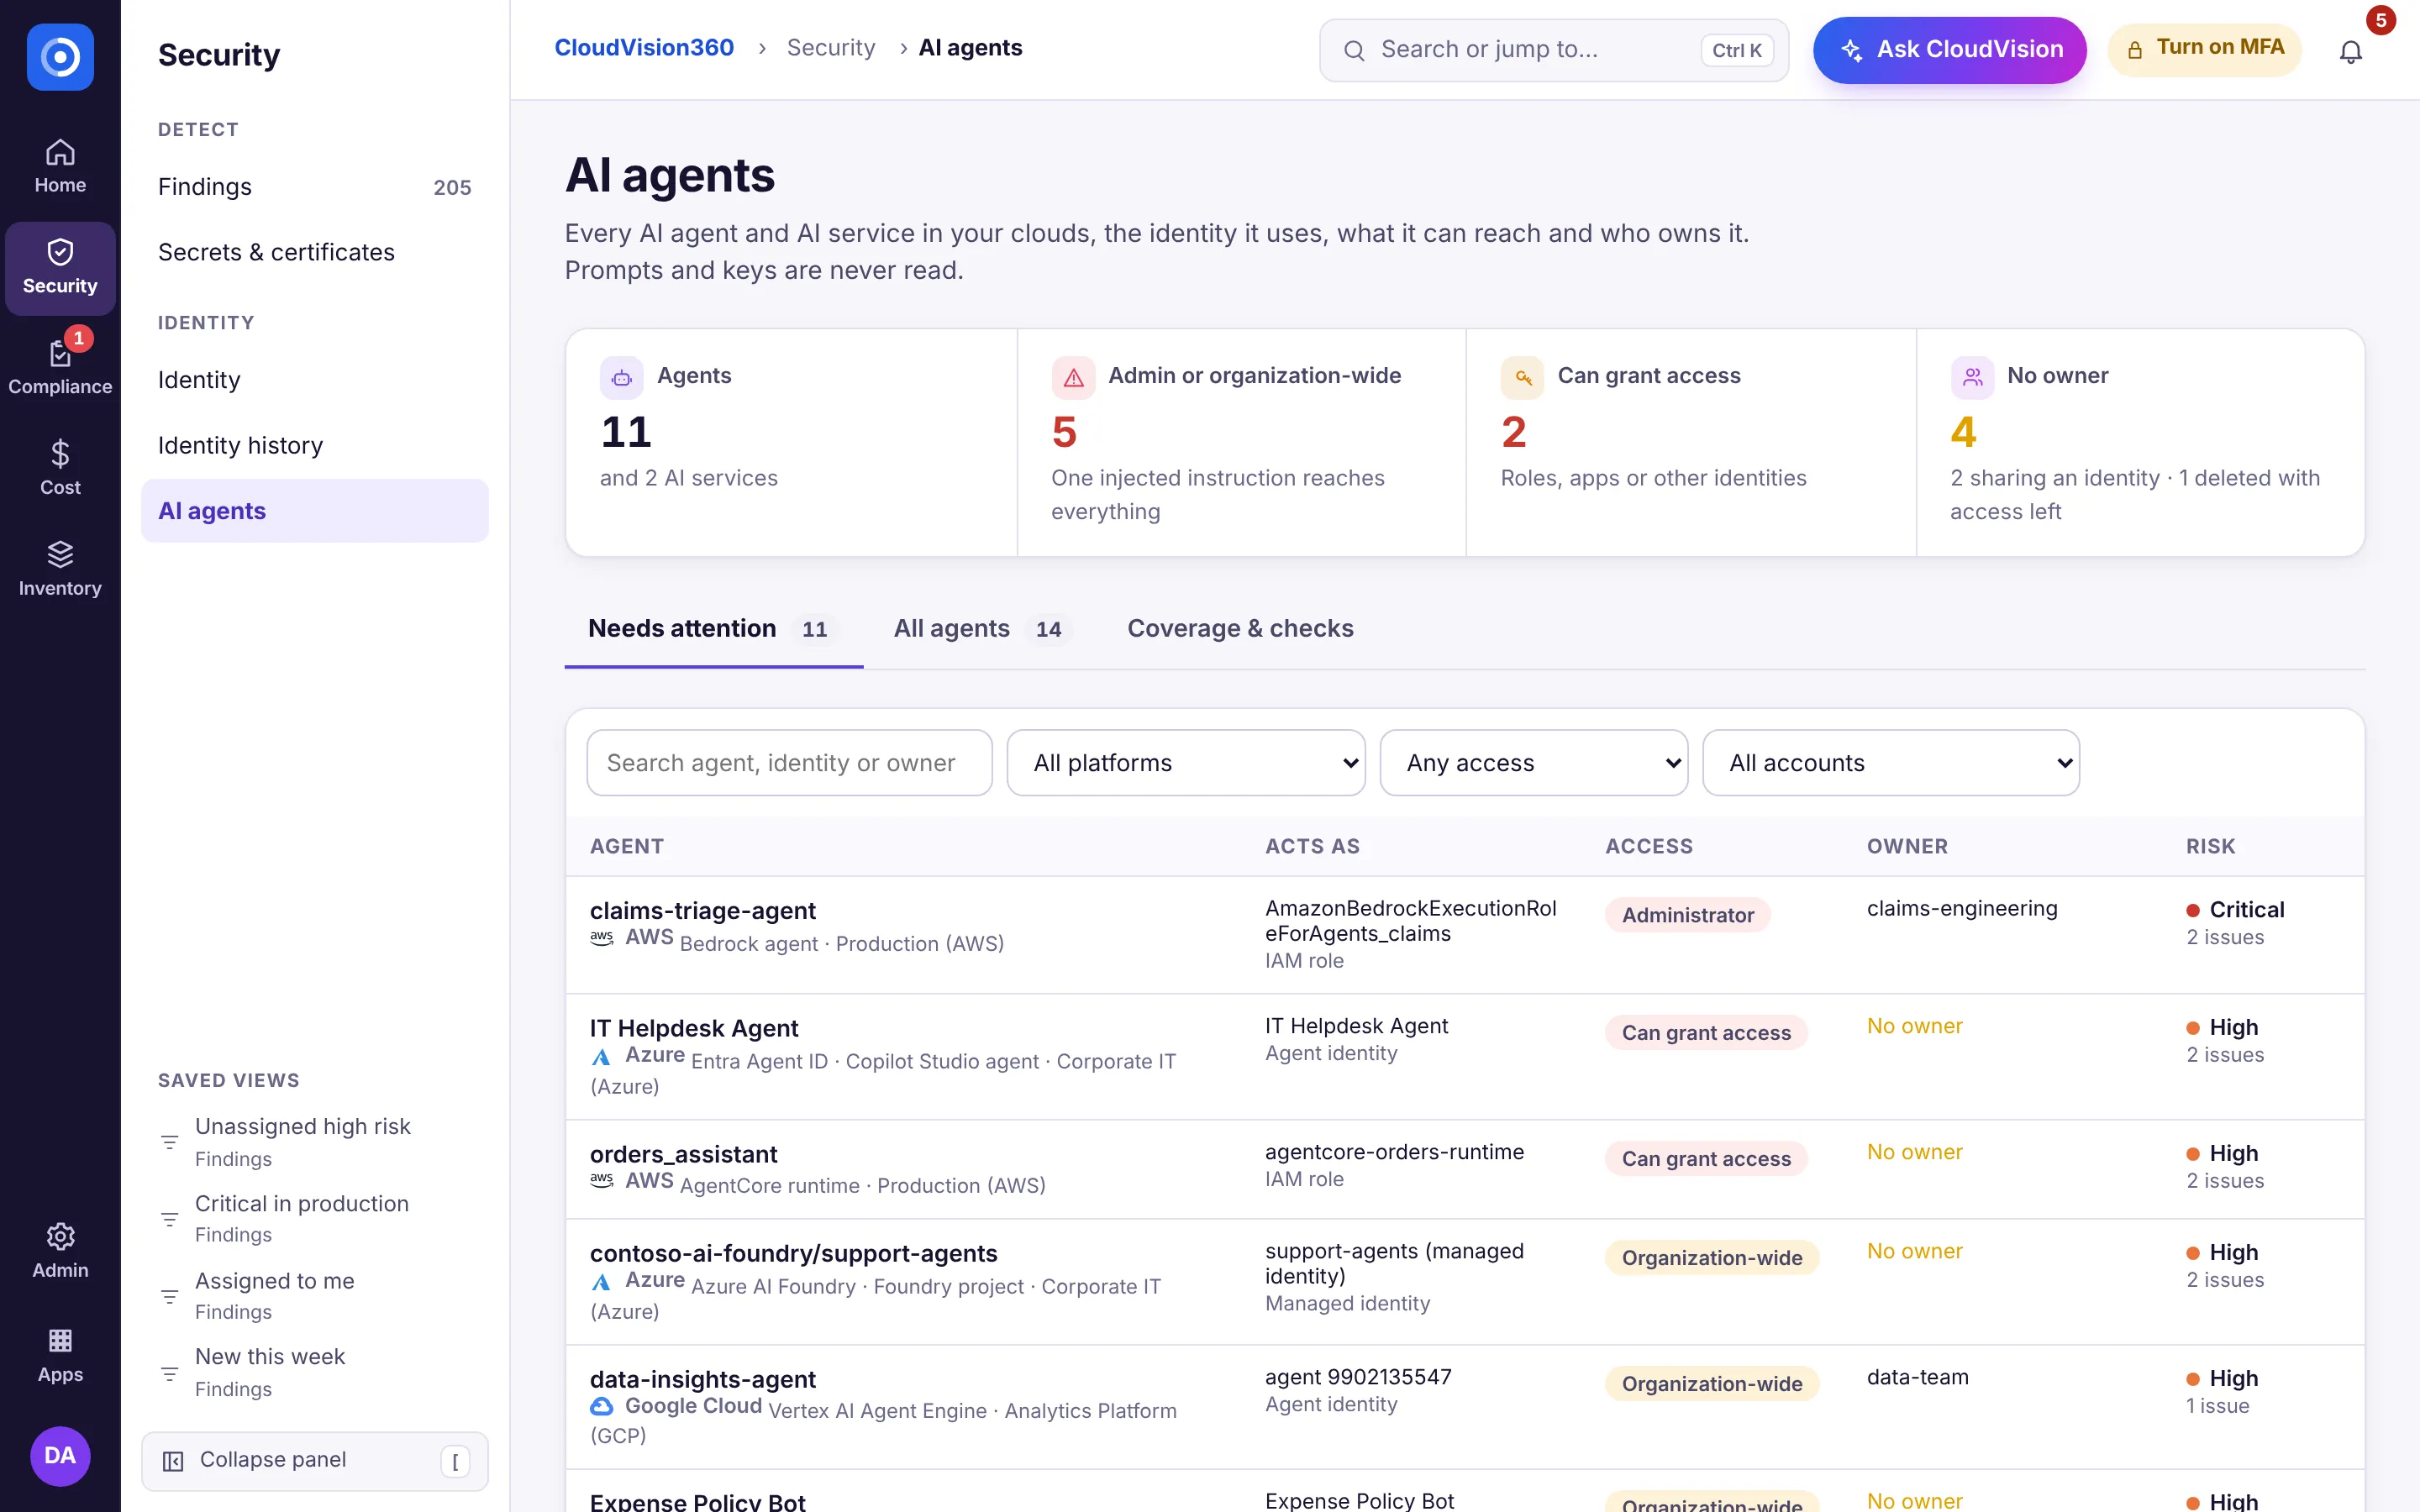
Open Security → AI agents to review agents by platform, privilege and owner, and to act on over-privileged or orphaned agents. For governing the AI that CloudVision360 itself uses, see Ask CloudVision and the AI gateway.