Attack-path analysis
Trace how an exposure on one asset could reach your crown jewels, reading posture only — never touching an exploit.
Online version, always current: https://cloudvision360.com/docs/itops360/attack-path-analysis/
A single low-severity issue matters a great deal if it sits on the path to something critical. Attack-path analysis shows those paths.
What it does
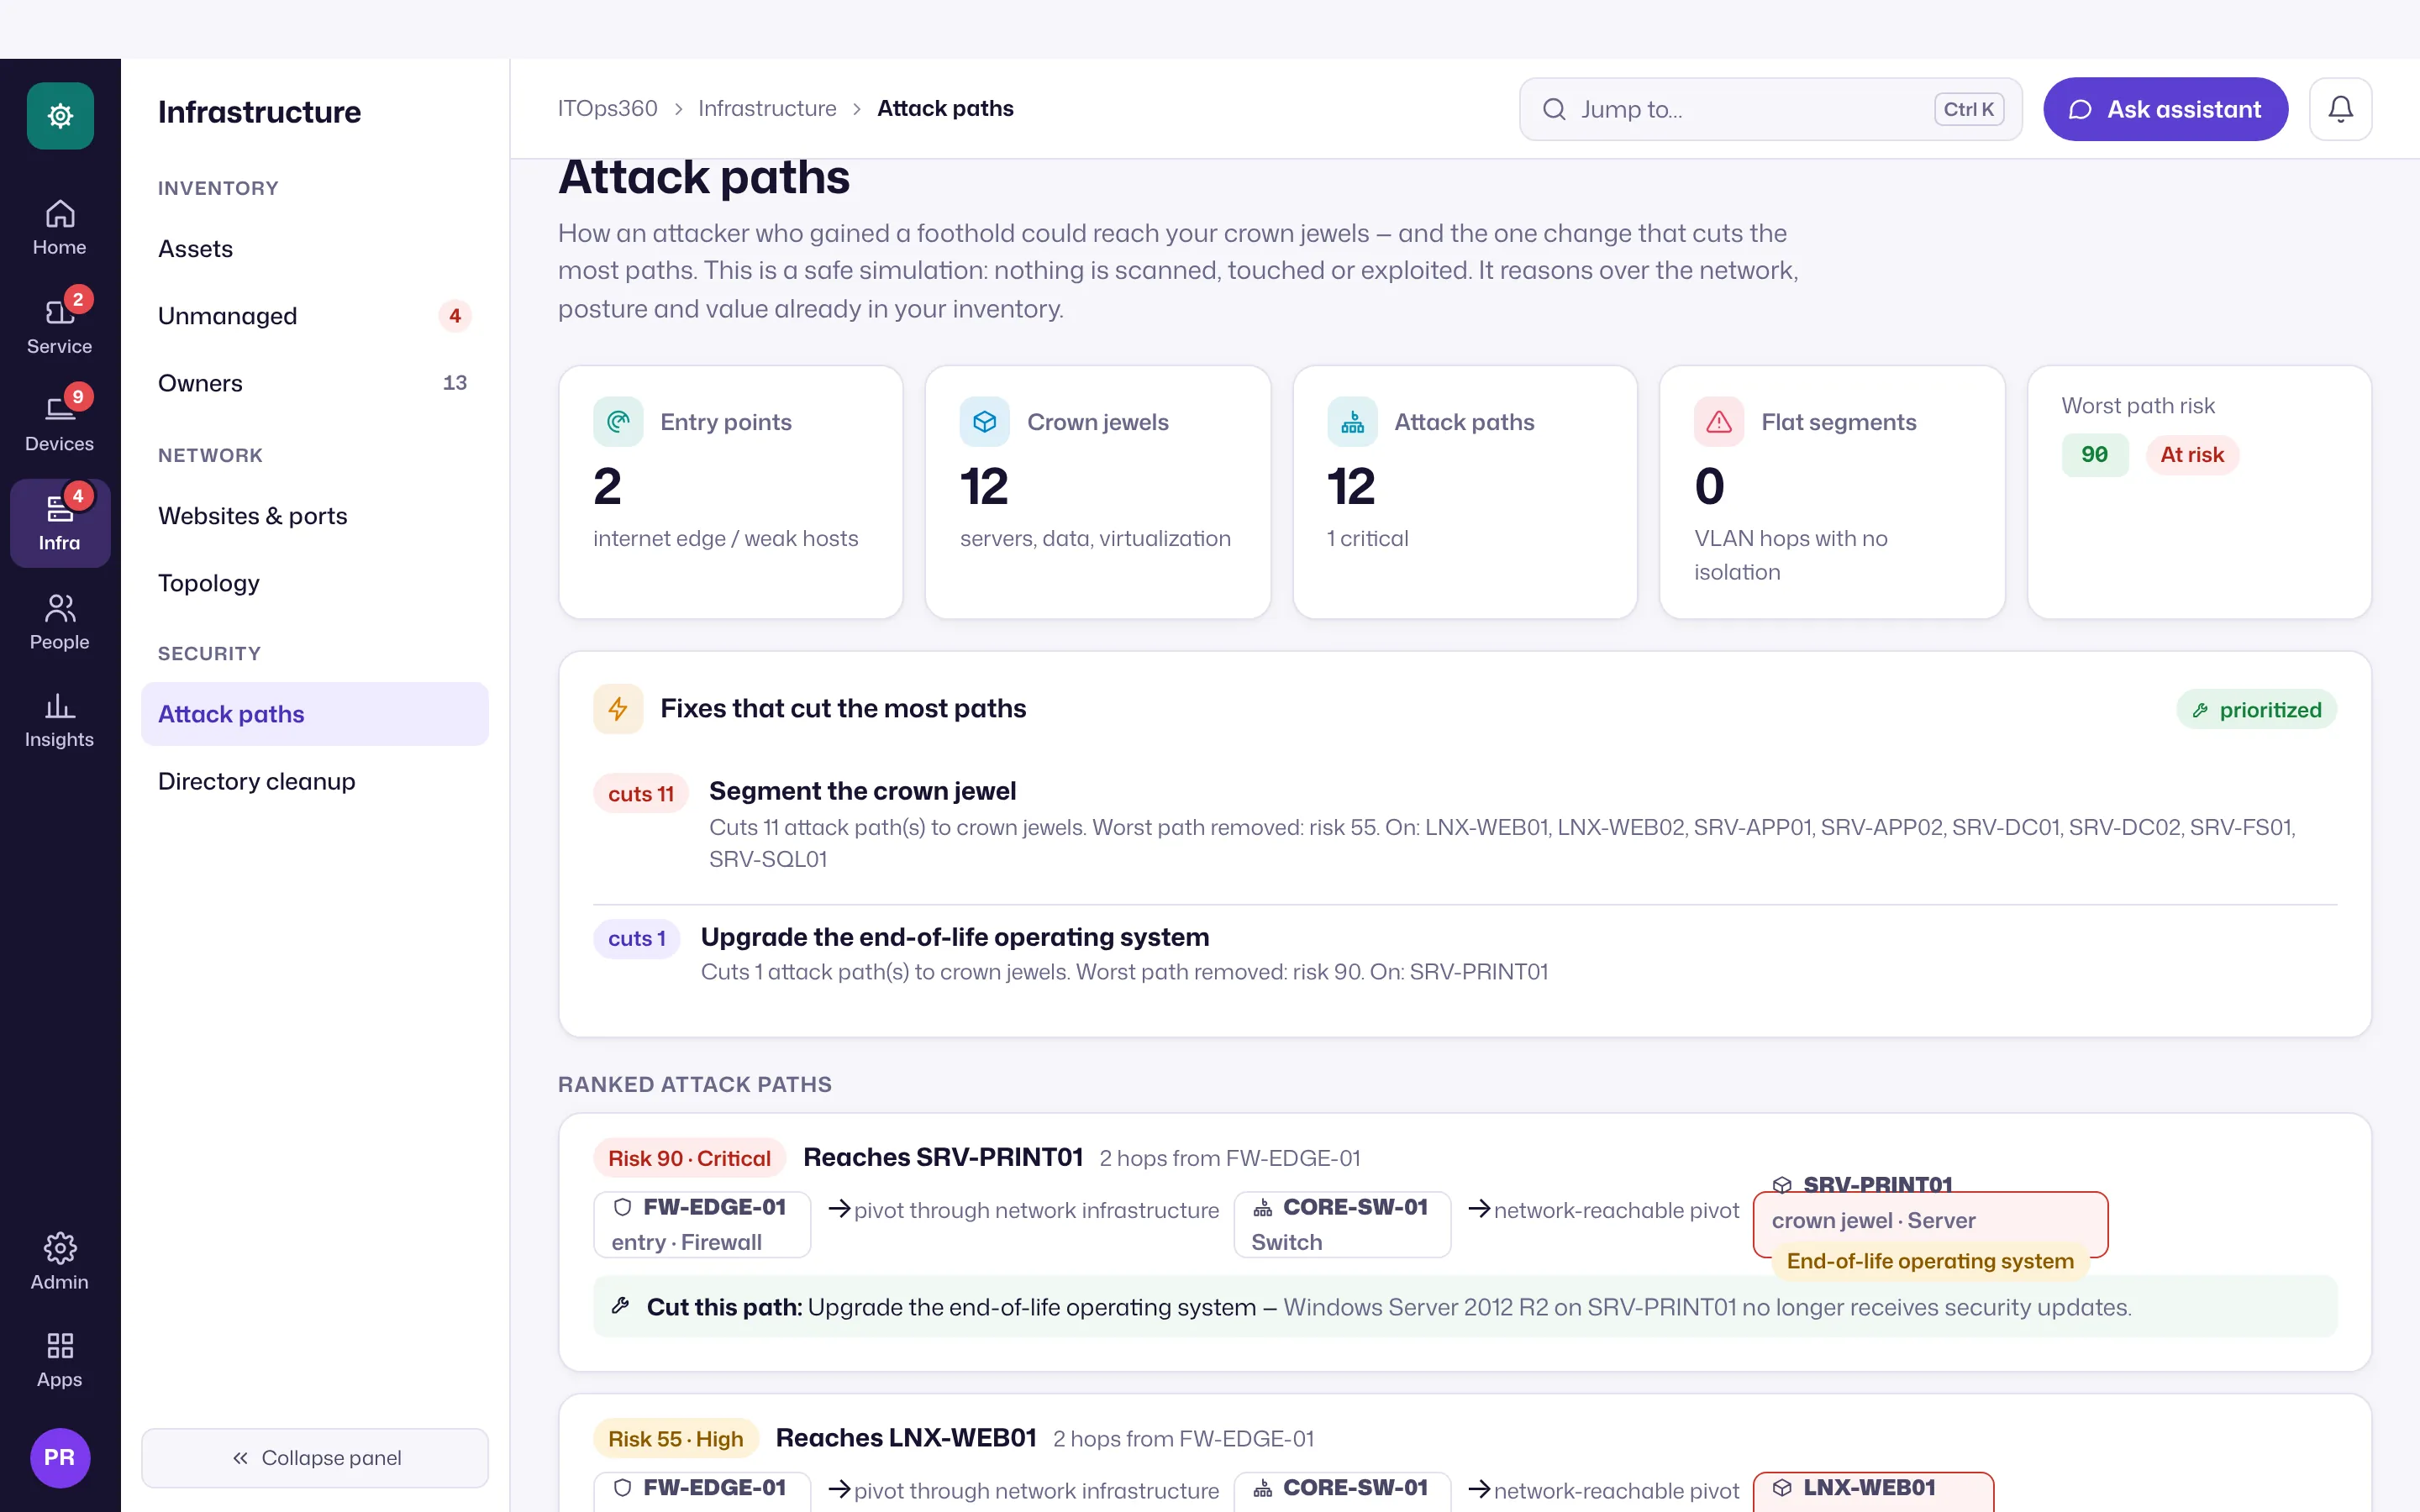
It traces how an exposure on one asset could be chained to reach your crown jewels — the systems and data that matter most — across the discovered estate. The result is a path, not just a list of isolated findings, so you can see which exposure to close to break the chain.
Posture only, never the exploit
Attack-path analysis reads posture only. It never touches, runs or simulates an exploit — it reasons over configuration and connectivity data that ITOps360 already has. It is analysis, not an attack.
Use it
Open Infrastructure → Attack paths to see the paths to your most critical assets, ranked by how exposed each is, with the specific step on each path that, if fixed, breaks it. Fixes run through governed automation.