Compliance frameworks
Evaluate common controls once from live data and map them to every framework your auditors ask for.
Online version, always current: https://cloudvision360.com/docs/cloudvision360/compliance-frameworks/
Compliance should be continuous, not a quarterly scramble of screenshots. CloudVision360 evaluates controls from live configuration and identity data and keeps the evidence current.
Map once, report many
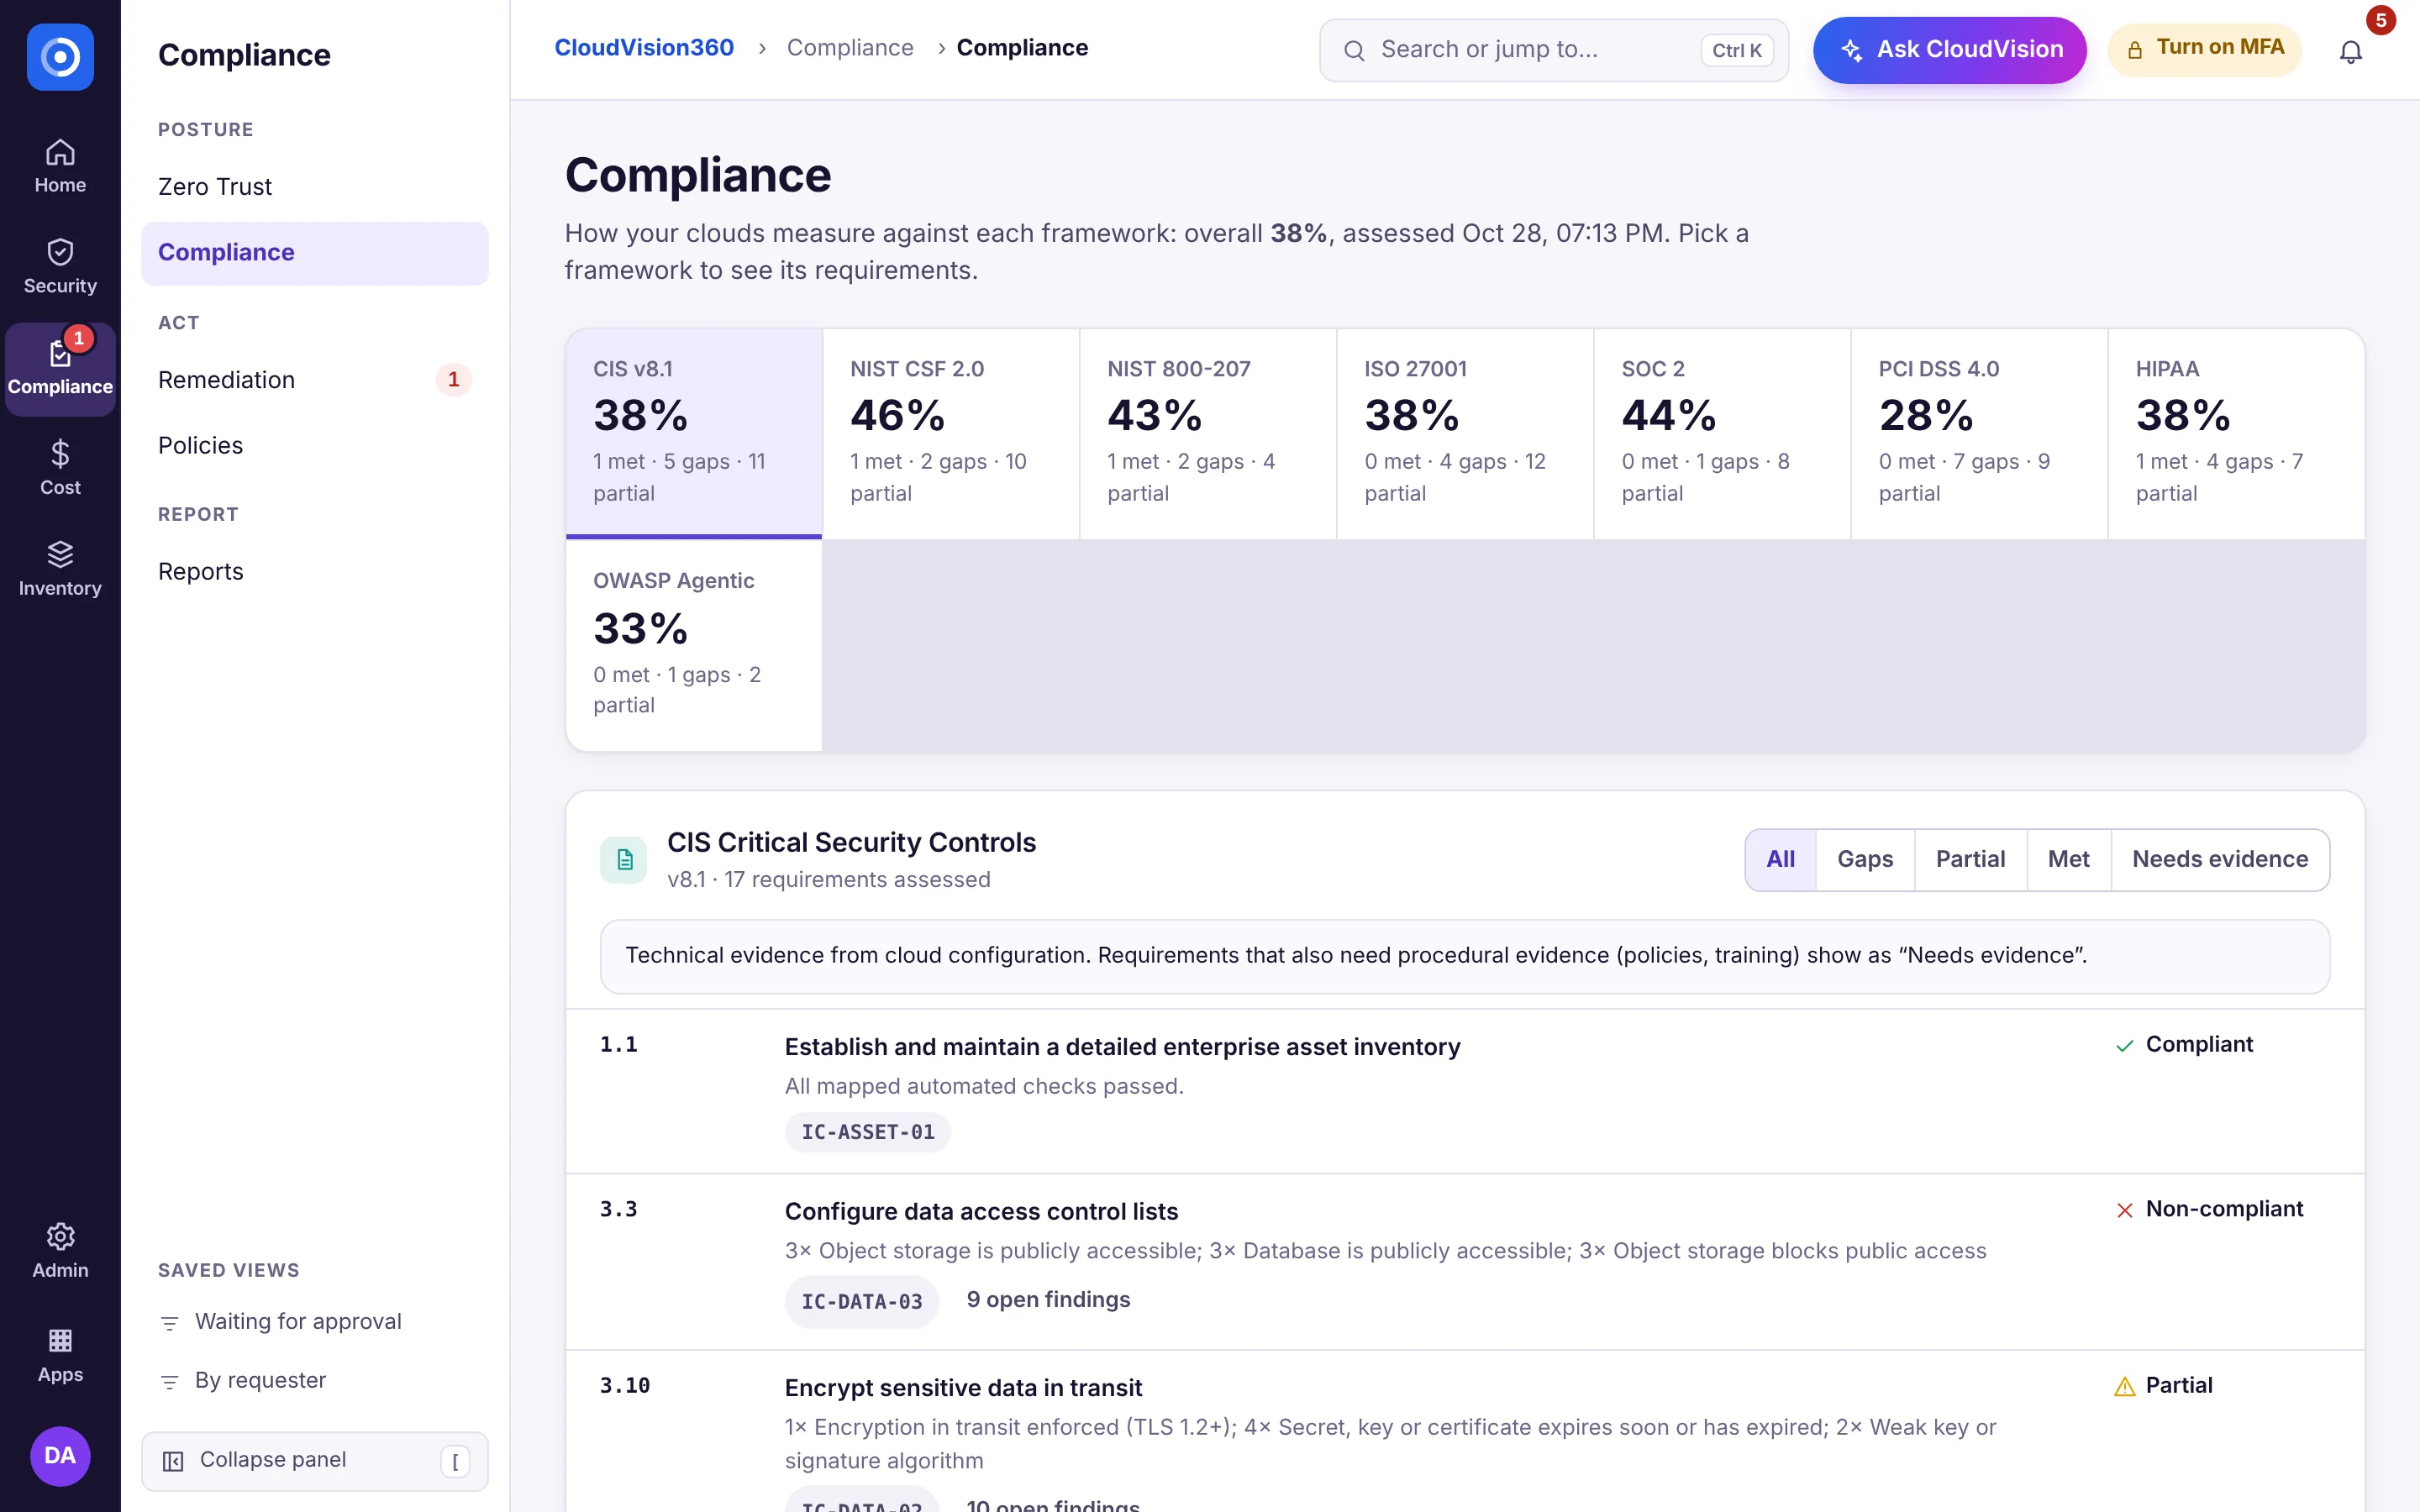
26 common controls are evaluated from your live data and mapped to each framework’s requirements, so you assess once and report against many. Supported frameworks include CIS Benchmarks, NIST CSF, NIST SP 800-207, ISO/IEC 27001, SOC 2, PCI DSS and HIPAA, plus the Gulf regulatory packs.
Evidence that stays current
Every scan refreshes control evidence. When drift breaks a control, it appears at once as a change, a finding and a compliance gap, so there is no lag between reality and your posture.
Honest about what software cannot prove
Procedural requirements — policies, training, physical controls — are flagged as needing evidence rather than marked as passed. A control the software cannot verify is never silently counted as met.
Accepted risk counted separately
Approved risk exceptions are shown as such, so a compliance score never hides accepted risk.
See where you stand
Open Compliance → Compliance, choose a framework, and see each requirement’s status, the live checks behind it, and the gaps ranked with the fix that closes each one. Export the result as a report.
On the roadmap
NIST AI RMF and ISO/IEC 42001 mappings are planned for AI governance.