Identity inventory and risk
Every human and machine identity across Entra ID, AWS IAM and Google IAM, with privilege, MFA, activity and configuration history.
Online version, always current: https://cloudvision360.com/docs/cloudvision360/identity-inventory/
Privilege accumulates across clouds and directories faster than anyone reviews it. CloudVision360 puts every identity that can reach production in one place.
Human and machine
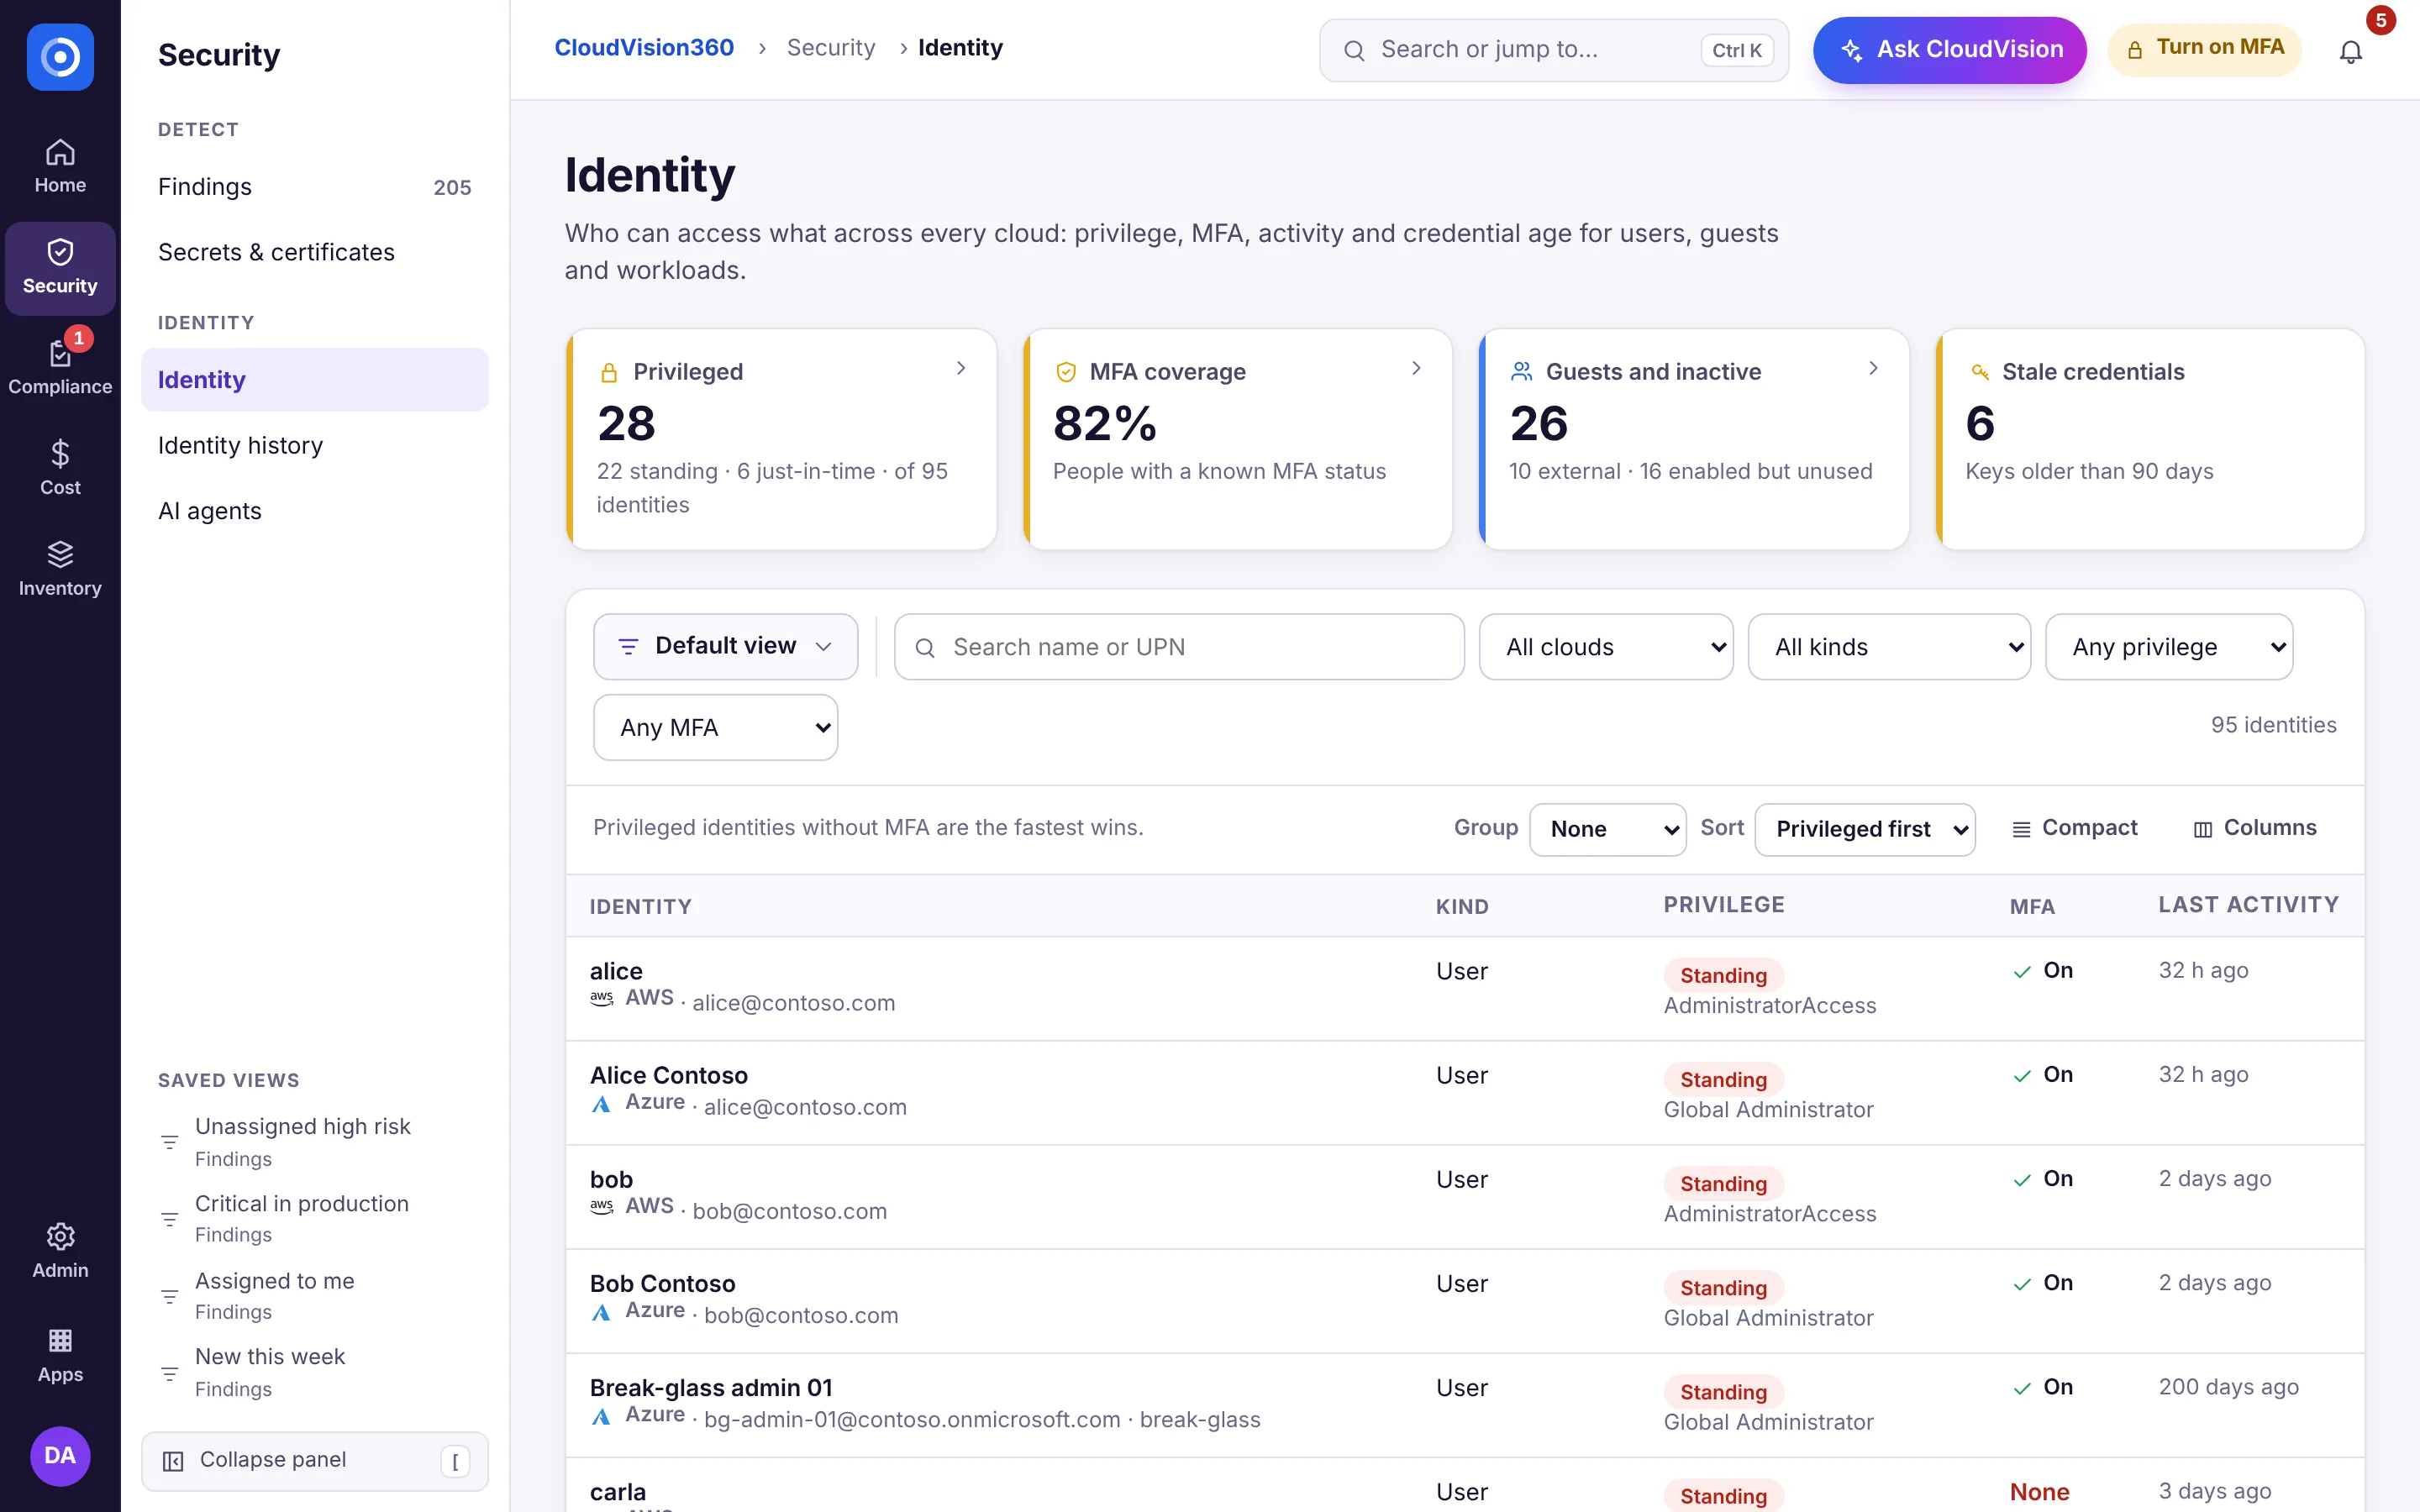
Users, guests, service principals, service accounts and applications across Microsoft Entra ID, AWS IAM and Google IAM — each with its privilege mode, MFA status, last activity and credential age.
Standing versus eligible
See who holds permanent privilege and who uses just-in-time elevation, so you can drive standing privilege down. Identities with permissions that can change security, identity or data are flagged as high-risk and scored.
Identity findings are security findings
Missing MFA, standing privilege, external guests, inactive accounts and stale keys appear as findings alongside the infrastructure they can reach, on one Fix first list.
Configuration history
Every change to Conditional Access, admin roles, IAM policies, trust relationships and IAM bindings is kept, compared and checked for risk — with a reviewed, two-person way back to the earlier configuration if a change should be undone.
Review
Open Security → Identity to filter by privilege, provider, MFA state or activity, and to run access reviews on guests and stale accounts. For emergency access when a JIT broker is down, see break-glass.